The Impact of PCI DSS 4.0 Compliance Deadlines on Independent Online Retailer Payment Page Design
The Impact of PCI DSS 4.0 Compliance Deadlines on Independent Online Retailer Payment Page Design
Even if an independent online shop doesn’t hold a single card number directly, they have always had a huge obligation to protect payment data. With PCI DSS 4.0, that responsibility has grown more detailed, notably concerning the online pages where users submit their payment details. The older version of the standard was deprecated and a series of requirements with future effective dates became necessary in early 2025, which put considerable pressure on small retailers to rethink how their checkout pages are constructed. Two requirements in particular are targeted at scripts that run in the browser of the consumer, reflecting the development of skimming attacks that steal card data directly from payment forms. For store owners who do not have big security teams, these changes impact design considerations, vendor selection, and ongoing maintenance. “Knowing what’s now expected helps retailers stay compliant and keep checkout quick and trustworthy.
Why PCI DSS 4.0 Changed the Rules for Payment Pages
The new standard was developed to address modern threats more effectively than the older standard could. Instead of attacking the merchant’s server, attackers increasingly target the customer’s browser, injecting malicious code into checkout pages to grab card credentials as they are keyed in. In response, the new version requires merchants to control and monitor the scripts that load on payment pages, not simply the servers hosting those pages. It also offers a more flexible approach, which allows businesses to achieve objectives with tailored approaches when they can demonstrate similar security. For independent shops, the key message is that the payment page itself is now a well defined area of compliance and how it is designed will directly impact how difficult or simple validation will be.
What Was Required and What Were the Key Dates
The transition period allowed organizations time to make changes, but the deadlines have past. Version 3.2.1 was retired in 2024 and the other forward dated criteria become necessary at the end of March 2025. This means that now all merchants with an annual evaluation or self-assessment questionnaire are obliged to demonstrate compliance with the entire set of controls. Retailers who delayed in getting ready may find that their acquiring banks and payment providers ask them for proof that they have script inventories, change detection and enhanced authentication. These expectations are live, so the practical question is not when to start, but how fast can gaps be corrected without impacting sales or customer experience.
Checkout Page Script Management and Integrity
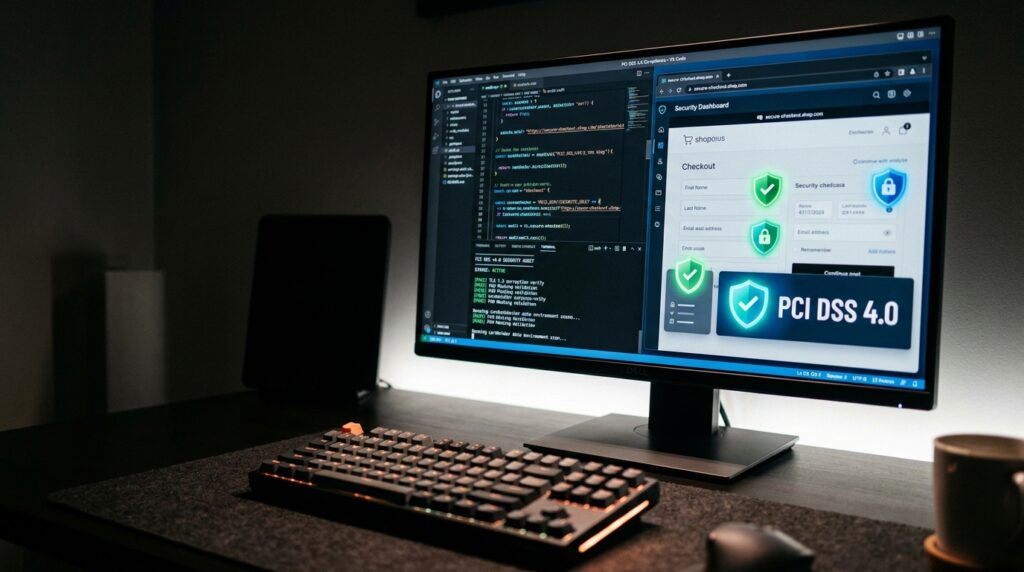
One of the most noticeable new requirements is that merchants must record an inventory of every code that loads on a payment page, along with a written rationale for why each one is necessary. Merchants must also verify that each script is permitted and has some type of integrity protection, such as a confirmed hash or a content security policy. In reality this encourages a leaner design. Tools for analytics, chat widgets, advertising pixels, social buttons used to be loaded on every page now they need to be reviewed carefully on checkout screens Less needless third-party code equals less compliance burden and less load time, which means better conversion and security.
Detecting Unauthorized Modifications to Payment Pages
There is also a way to warn staff of any illegal modifications to the content and headers of the payment pages and check them at least weekly or as determined by a documented risk analysis. The goal is to find skimming code as soon as it emerges. Independent shops can satisfy the criteria by using monitoring services, security plugins or tools given by their hosting and payment providers. Alerts need to be responded to. That involves assigning someone to be clearly responsible for responding. Stable and simple page design makes change detection more accurate. Fewer valid updates imply fewer false alarms and faster analysis of true problems.
Hosted Fields, Redirects, and Selecting a More Secure Payment Architecture
The manner a business stores card data most impacts the scope of compliance. When customers are fully redirected to a payment provider’s hosted page, card entry doesn’t occur within the merchant’s environment. When hosted fields or embedded frames are provided by a payment provider, the sensitive inputs are isolated in a separate secure container. Both of these methods limit the risk compared to designing a bespoke form that directly handles card data. The new standard still requires merchants utilizing embedded frames to protect the surrounding site and verify that it cannot be updated to interfere with the payment process. For a small retailer, the single best design option is often to pick a well-supported provider and a simple integration architecture.
Authentication, Access Control, & Operational Requirements
Several changes will effect the people and systems that administer the store, not the page itself. The new standard includes stronger password restrictions, more usage of multi-factor authentication to access the cardholder data environment, and more controls on administrative accounts. For small teams, this implies multi-factor protection for the e-commerce platform, hosting panel, payment dashboard, and any tool that can modify checkout code. Shared logins should be deleted, access should only be given to those who actually require it. These methods indirectly protect the payment page as attackers commonly get access through compromised administrator credentials and then inject dangerous code.
Cooperation with Payment Providers and Third Party Vendors
Independent stores rarely go it alone on compliance, and the standard acknowledges joint responsibilities for merchants and service providers. Retailers should ask their payment gateway, hosting provider and platform vendor to clarify what controls they administer and which are the merchant’s responsibility. Having written responsibility matrices and current compliance documentation makes completing audits and questionnaires so much easier. There’s a lot of companies that have script monitoring built in today, security headers and guidance for small organizations. By selecting providers who are already working on the updated criteria, you can save a lot of time and cost. In contrast, poorly supported plugins or obsolete themes often create hidden compliance gaps that are difficult to fix later.
Creating a Sustainable Compliance Routine for Small Retailers
Compliance is not a one-off activity, the most successful independent retailers make it a routine. This means checking the script inventory whenever marketing tools or plugins are introduced, evaluating the payment page after any major update, and keeping the program patched. Documentation of decisions, assigning duties and arranging regular reviews provide the proof assessors and acquiring banks look for. A straightforward well described checkout design makes each of these duties easy. This rigorous approach protects customers against skimming assaults, lowers the likelihood of costly breaches, and builds lasting confidence in a retailer’s brand.